
Can a business protect personal information properly without clear principles guiding how data is handled? Organisations regularly collect information about customers, employees and suppliers, making responsible data practices essential. GDPR Course can help professionals understand the principles that guide lawful and responsible processing. These principles influence how information is collected, used, stored and protected.
Following them can also help businesses create consistent privacy practices. In this blog, let us explore the GDPR Data Protection principles every business should understand and follow when managing personal information.
Table of Contents
- Key GDPR Data Protection Principles Every Business Should Follow
- Why Following These Principles Matters
- Conclusion
Key GDPR Data Protection Principles Every Business Should Follow
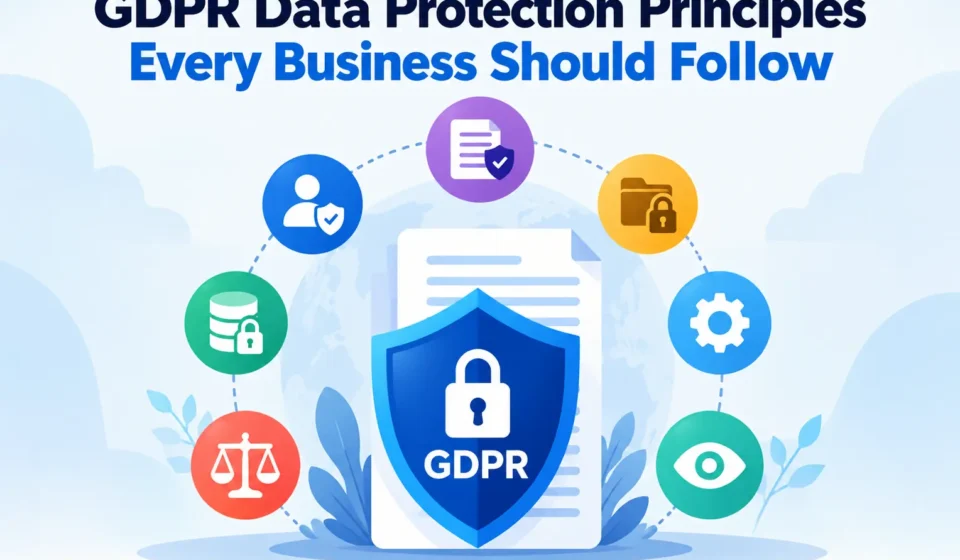
Below are the seven key GDPR Data Protection principles that guide businesses in collecting, using, storing and protecting personal information responsibly while supporting stronger GDPR Compliance:
Lawfulness, Fairness and Transparency
Businesses must have a Lawfulness for collecting and processing personal information. They should also handle data fairly and clearly explain how it will be used. People should not be left uncertain about what happens to their information after they provide it.
Clear privacy information can help businesses explain the purpose of Data Processing, how long information may be retained and who may receive it. Transparent practices also help individuals understand how their personal data is being handled.
Purpose Limitation
Personal information should be gathered for precise, understandable, and legal purposes. Before requesting specific information from clients or other people, businesses must understand why it is necessary.
Reusing information for unrelated purposes without taking GDPR regulations into account is not acceptable. Professionals can learn how purpose limitation affects routine data handling decisions and promotes safe use of personal data by taking a GDPR Course.
Data Minimisation
Businesses should collect only the personal information that is relevant and necessary for a particular purpose. Gathering excessive information can increase privacy concerns and Data Protection Risks.
Regular reviews can help organisations identify information that is no longer necessary. Data Minimisation reduces the volume of information businesses need to store, manage and protect. It can also reduce potential exposure if a security incident occurs.
Accuracy
Personal information should be accurate and kept up to date where necessary. Incorrect or outdated records can cause communication problems and lead to decisions being made using unreliable information.
Businesses should have suitable processes for identifying and correcting inaccurate data. Individuals should also have appropriate ways to request corrections. Maintaining Data Accuracy improves the reliability of business records and supports responsible personal data management.
Storage Limitation
Personal information shouldn’t be retained by businesses for longer than is necessary. The purpose for which the data was gathered and any applicable operational or legal requirements may determine the proper retention period.
Organisations can determine how long various kinds of information should be kept on file with the use of a clear data retention policy. Frequent evaluations are also crucial. When information is no longer needed, it should be safely erased or, if necessary, anonymised.
Integrity and Confidentiality
Personal data must be adequately safeguarded against unauthorised access, destruction, alteration, or disclosure. Companies should take into account the risks connected to the data they handle and implement appropriate security measures.
Access restrictions, secure systems and frequent security reviews are some examples of strong data security. Professionals can learn about their obligations while accessing, storing, or sharing personal data by taking a GDPR Course.
Accountability
Businesses are responsible for complying with GDPR requirements and should be able to demonstrate the steps they take to protect personal information. Written policies alone may not be enough if they are not followed in everyday activities.
GDPR Accountability can involve maintaining appropriate records, assessing data protection risks and providing relevant employee training. Clear responsibilities can also help employees understand what they need to do when handling personal information.
Why Following These Principles Matters
In order to establish a basis for responsible data protection, the seven principles function in conjunction with one another.
From the moment that personal information is obtained until it is either anonymised or removed in a secure manner, they encourage businesses to consider data protection at every stage of the information lifecycle.
By constantly applying these principles, it is possible to decrease the gathering of data that is not necessary and strengthen security standards. Additionally, it has the potential to reduce confusion regarding privacy duties among various teams and commercial operations.
Conclusion
The GDPR Data Protection principles give businesses a clear foundation for handling personal information responsibly. Following them can improve transparency, reduce unnecessary data collection, strengthen security and create more consistent privacy practices. They also help organisations consider data protection throughout the complete information lifecycle.
The Knowledge Academy, a trusted global training provider for GDPR Courses, helps professionals build practical skills for responsible data handling and stronger GDPR Compliance.